Discover Level Blue’s main solutions:
Security Information and Event Management (SIEM)
Everything you need to Detect and Respond to Advanced Threats, plus SIEM and Log Management.
Single-purpose SIEM software solutions and log management tools provide valuable security insights, but they often require costly and time-consuming integration efforts to bring in log files from disparate sources, such as asset inventory, vulnerability assessment, endpoint agents, and IDS products. Once you have the data, you must search for and write correlation rules to identify threats in your environment. These challenges multiply as you migrate workloads and services from on-premises infrastructure to public cloud environments.
For today’s resource-constrained IT teams, the time and expense required to deploy a SIEM seriously delays time to threat detection and, therefore, return on investment.
Key Benefits of AT&T Cybersecurity SIEMs:
| Features | AlienVault USM | Traditional SIEM |
|---|---|---|
| Management: | ||
| Records Management | ✓ | ✓ |
| Event management | ✓ | ✓ |
| Event correlation | ✓ | ✓ |
| Communicating | ✓ | ✓ |
| Management: | ||
| Resource discovery | ✓ | $ Requires Integration $ |
| Network IDs | ✓ | $ Requires Integration $ |
| Host ID | ✓ | $ Requires Integration $ |
| File Integrity Monitoring | ✓ | $ Requires Integration $ |
| Cloud Monitoring (AWS, Azure, Office 365, G Suite) | ✓ | $ Requires Integration $ |
| Incident Response (AlienApps) with Third-Party Security and Operations Tools | ✓ | $ Requires Integration $ |
| Vulnerability assessment | ✓ | $ Requires Integration $ |
| Endpoint Detection and Response | ✓ | $ Requires Integration $ |
| Security monitoring technologies: | ||
| Continuous Threat Intelligence | ✓ | Not available |
| Unified management console for security monitoring technologies | ✓ | Not available |
USM AnyWhere
USM Anywhere is a highly extensible platform that leverages AlienApps—modular software components tightly integrated into the USM Anywhere platform that extend, orchestrate, and automate functionality between the security controls built into USM Anywhere and other third-party security and productivity tools.
USM Anywhere centralizes security monitoring of networks and devices in the cloud, on-premises, and remote locations, helping you detect threats virtually anywhere.
Discovery in:
- Network assets
- Software and services
- AWS assets
- Azure assets
- Google Cloud Platform assets
Analytics:
- SIEM event correlation
- Auto-prioritized alarms
- User activity monitoring
- Up to 90 days of online, searchable events
Detection:
- Cloud intrusion (AWS, Azure, GCP)
- Network intrusion (NIDS)
- Host intrusion (HIDS)
- Endpoint detection and response (EDR)
Response:
- Forensic inquiry
- Response automation and orchestration
- Notifications and ticketing
Assessment:
- Vulnerability scanning
- Cloud infrastructure assessment
- User and asset configuration
- Dark web monitoring
Reporting:
- Pre-built compliance template
- Pre-built event template
- Customizable visualizations and dashboards
- Log storage

How does the platform work?
Focus on real threats by starting to monitor on day one.
Intelligent, automated data collection and analysis
USM Anywhere automatically collects and analyzes data across your entire attack surface, helping you quickly gain centralized security visibility without the complexity of multiple disparate security technologies.
Automated threat detection powered by AT&T Alien Labs
With threat intelligence provided by AT&T Alien Labs, USM Anywhere automatically updates to stay on top of evolving and emerging threats, so your team can focus on responding to alerts.
Incident response orchestration with AlienApps
USM AnyWhere supports a growing ecosystem of AlienApps, allowing you to orchestrate and automate actions across other security technologies so you can respond to incidents quickly and easily.
Watch the video | Product brochure
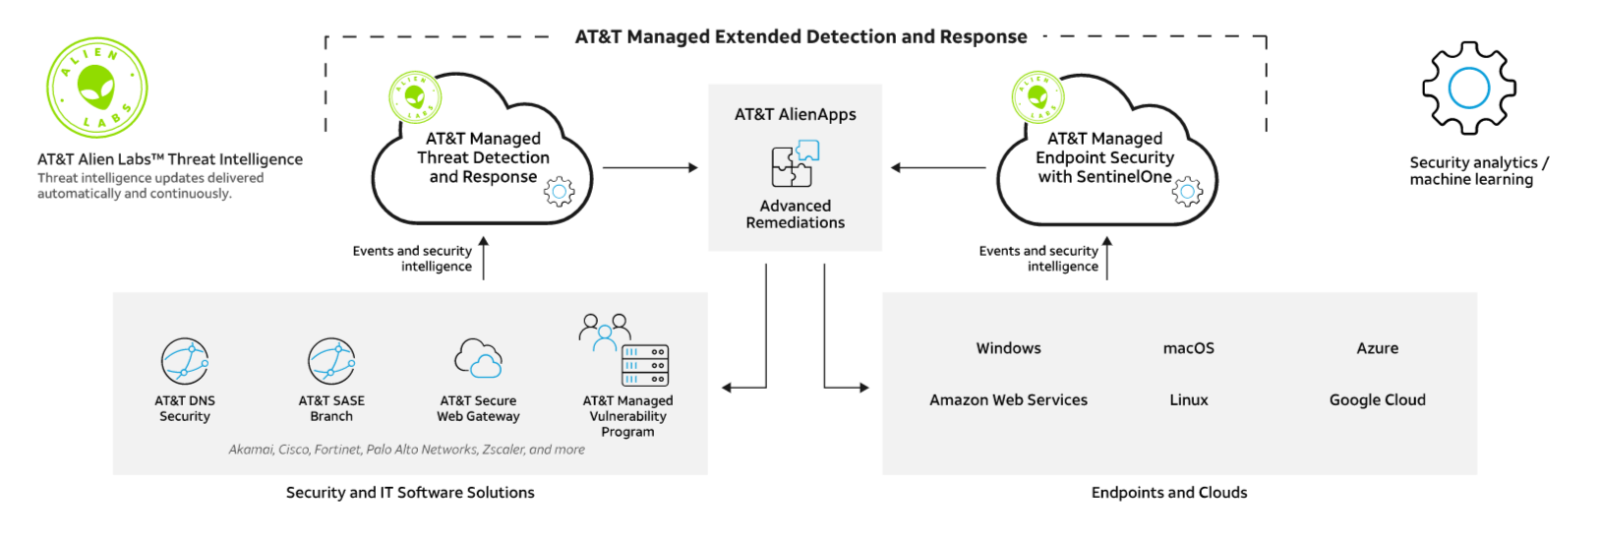
Extended Detection and Response (XDR)
AT&T’s solution encompasses telemetry and other attack data collection and uses security analytics and machine learning to drive better incident response.
Enpdoint Protection NextGen (SentinelOne)
Deliver next-generation protection for your customers’ endpoints. Autonomously and quickly detect and respond to sophisticated, ever-present cyber threats, while proactively hunting for new threats before they can take action.
How SentinelOne Benefits You
- Minimize dwell time
- Simplified experience
- Fast, automated remediation
- Reduce alert fatigue
- Expertise you can count on
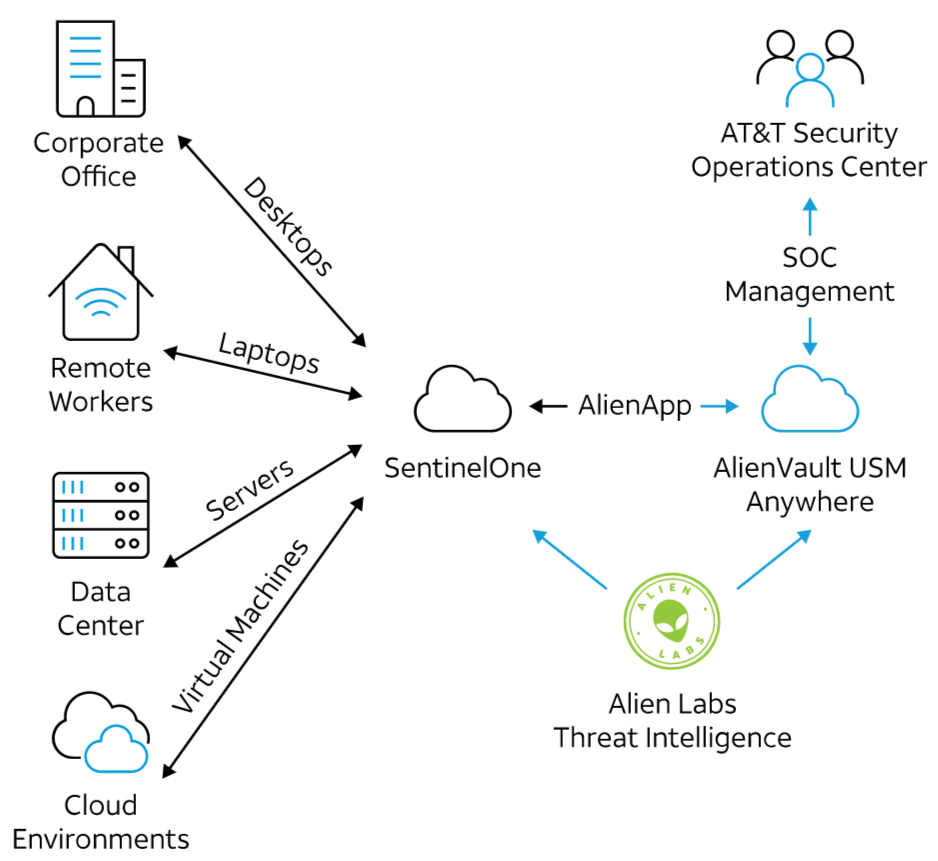
And you can still offer all AT&T solutions as a Service Provider (MSSP)!